
These 4 Android Apps Redirect Customers To Malicious Websites –
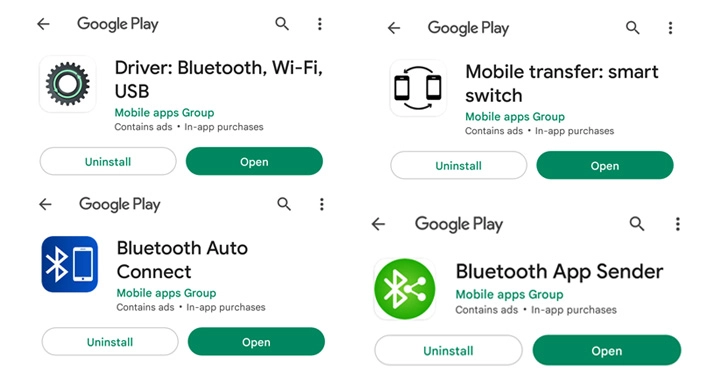
In line with the most recent experiences, a brand new set of 4 Android apps launched by the identical developer has been found directing customers to malicious web sites as a part of an adware and information-stealing marketing campaign. Lately, it has change into fairly widespread. So, beware whereas downloading something from anyplace.
Right here Is The Listing of Newly Discovered Malware Android Apps
These apps had been revealed by a developer named Cell apps Group and are presently out there on the Play Retailer. The attention-grabbing a part of the information is that they’ve been collectively downloaded over a million occasions. In line with the experiences by Malwarebytes, the web sites are designed to generate revenues by pay-per-click adverts. The more severe factor is that they immediate customers to put in cleaner apps on their telephones with the purpose of deploying extra malware.

The record of apps is as follows:
|
It’s not stunning in any respect. These days, malicious apps have devised new methods to get previous Google Play Retailer safety protections. One of the vital well-known ways adopted by risk actors is to introduce time-based delays to hide their malicious habits. Malwarebytes’ evaluation additionally discovered the apps to have an roughly four-day ready interval earlier than opening the primary phishing web site within the Chrome browser. After that, it proceeds to launch extra tabs each two hours.
Additionally Learn: Govt of Pakistan Formally Launches Nationwide On-line Passport Charge App – (phoneworld.com.pk)