
REvil ransomware group goes darkish after its Tor websites have been hijacked – TechCrunch
REvil, the infamous Russian-linked ransomware gang chargeable for the high-profile cyberattacks on Kaseya, Travelex, and JBS earlier this yr, has disappeared once more after its Tor fee portal and knowledge leak weblog have been allegedly hijacked.
The shutdown comes weeks after the group re-emerged following a months-long hiatus, throughout which the group went quiet after dealing with warmth from the U.S. authorities in response to its assault on Kaseya, which resulted in hundreds of corporations changing into contaminated with ransomware. Information of the shutdown was first claimed by a risk actor recognized to be affiliated with the REvil operation in a submit on a recognized prison discussion board, first found by Recorded Future’s Dmitry Smilyanets.
The risk actor’s submit mentioned the group’s Tor companies have been hijacked and changed with a replica of the group’s non-public keys, probably from an earlier backup. “The server was compromised and so they have been searching for me,” the submit reads. “To be exact, they deleted the trail to my hidden service within the torrc file [used for configuring the Tor service] and raised their very own in order that I’d go there. I checked on others — this was not. Good luck everybody, I’m off.”
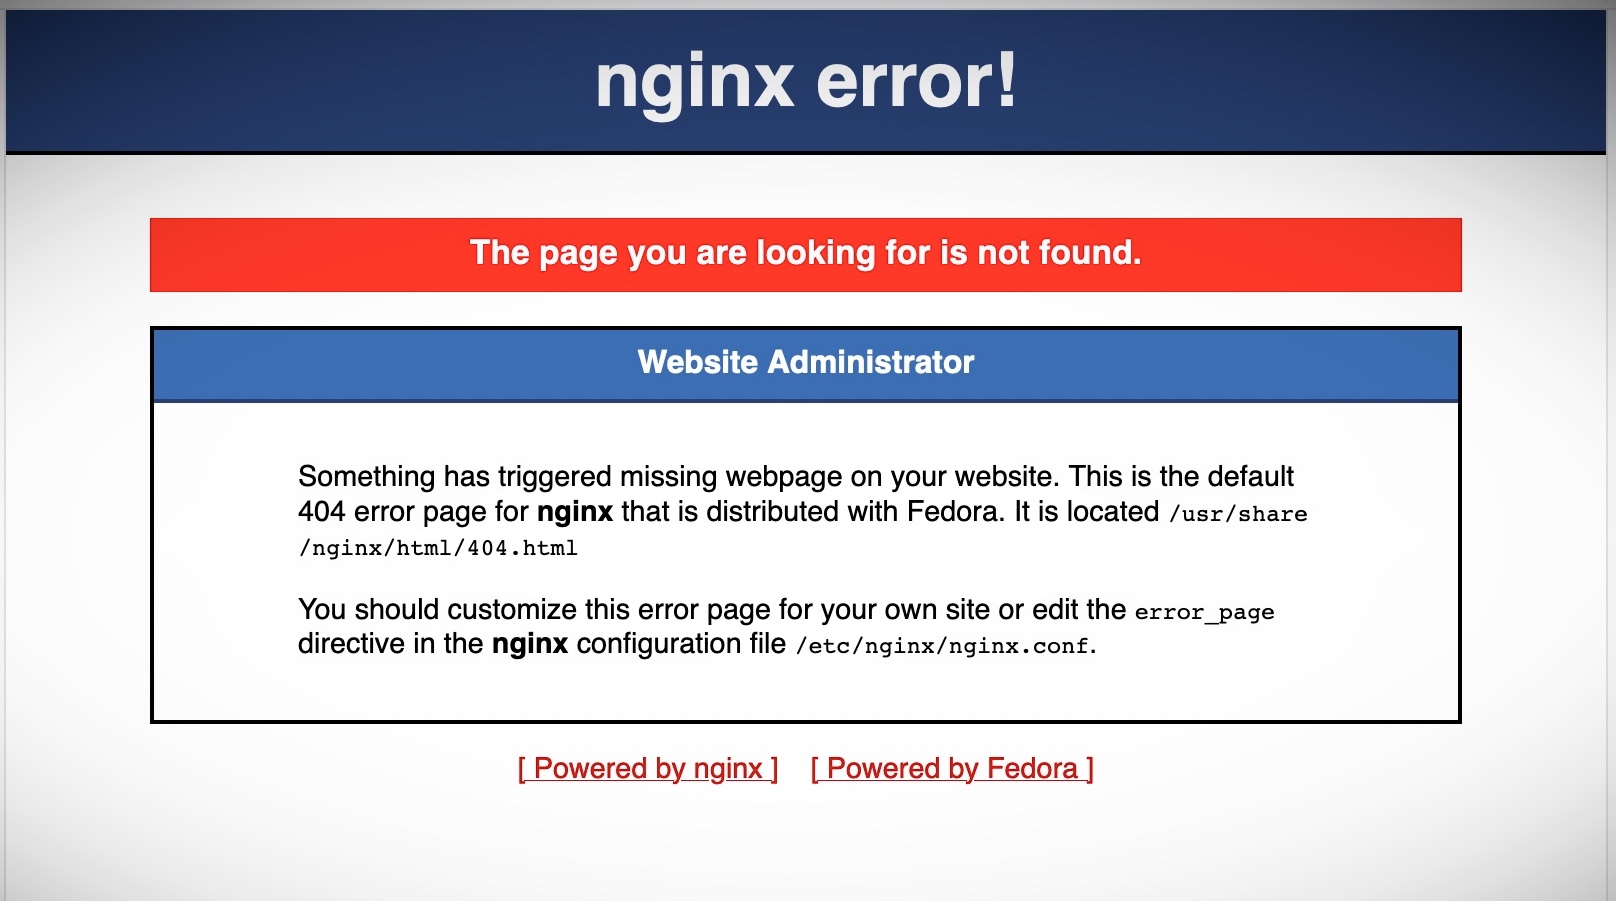
What REvil’s Tor website appears like on the time of publication following an obvious hijack. (Picture: TechCrunch)
On the time of writing, it isn’t clear who compromised REvil’s servers. A report by The Washington Publish in September mentioned the FBI had obtained the group’s encryption keys for the businesses hit by the Kaseya assault in July, however that the company’s deliberate takedown by no means occurred after the group disappeared. Others are pointing to a potential takeover by a former group member, often known as “Unkn,” or Unknown, a long-time spokesperson for the group, who didn’t return when the remainder of the group reemerged in September.
“Since there was no affirmation of the explanation for his loss, we resumed work, pondering that he was useless,” the risk actor defined of their discussion board submit. “However since we now have as we speak at 17.10 from 12:00 Moscow time, somebody introduced up the hidden-services of a touchdown and a bathroom with the identical key as ours, my fears have been involved.”
VX-Underground, a web site that hosts malware supply code, samples, and papers, tweeted that solely Unknown and the forum-posting risk actor had REvil area keys and that the ransomware group’s area was lately accessed utilizing Unknown’s keys.
It stays to be seen whether or not REvil — linked to nearly all of ransomware detections within the second quarter this yr, in accordance with McAfee — is gone for good. However because the group’s shock reappearance in September, it has struggled to recruit customers, prompting the group to increase its affiliate commissions to entice new risk actors.